A security expert from Securify spoke about the CVE-2018-17153 issue in the Western Digital network-attached storage (NAS), which the developers have been unable to fix since April 2017. The vulnerability allows you to bypass authentication and take control of the My Cloud as a device administrator.
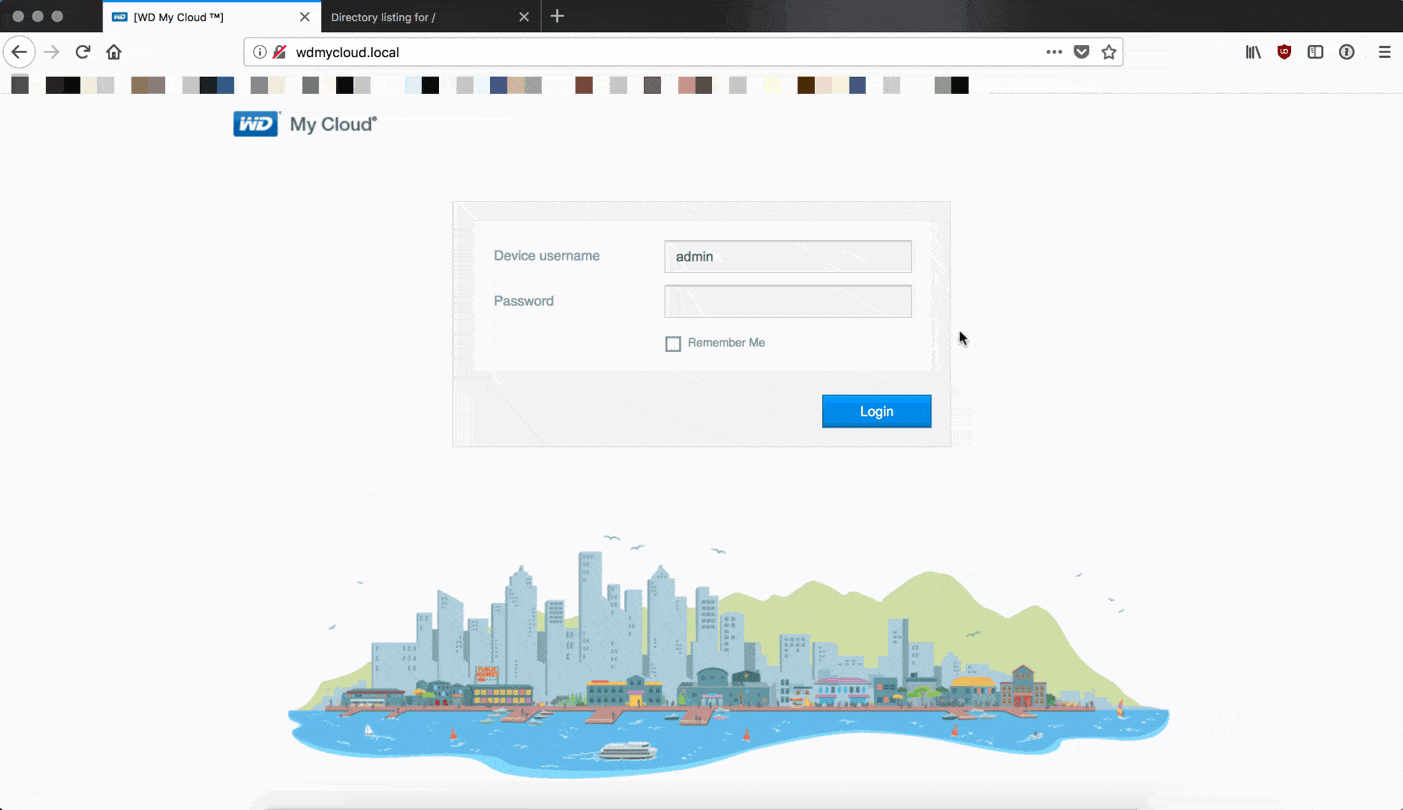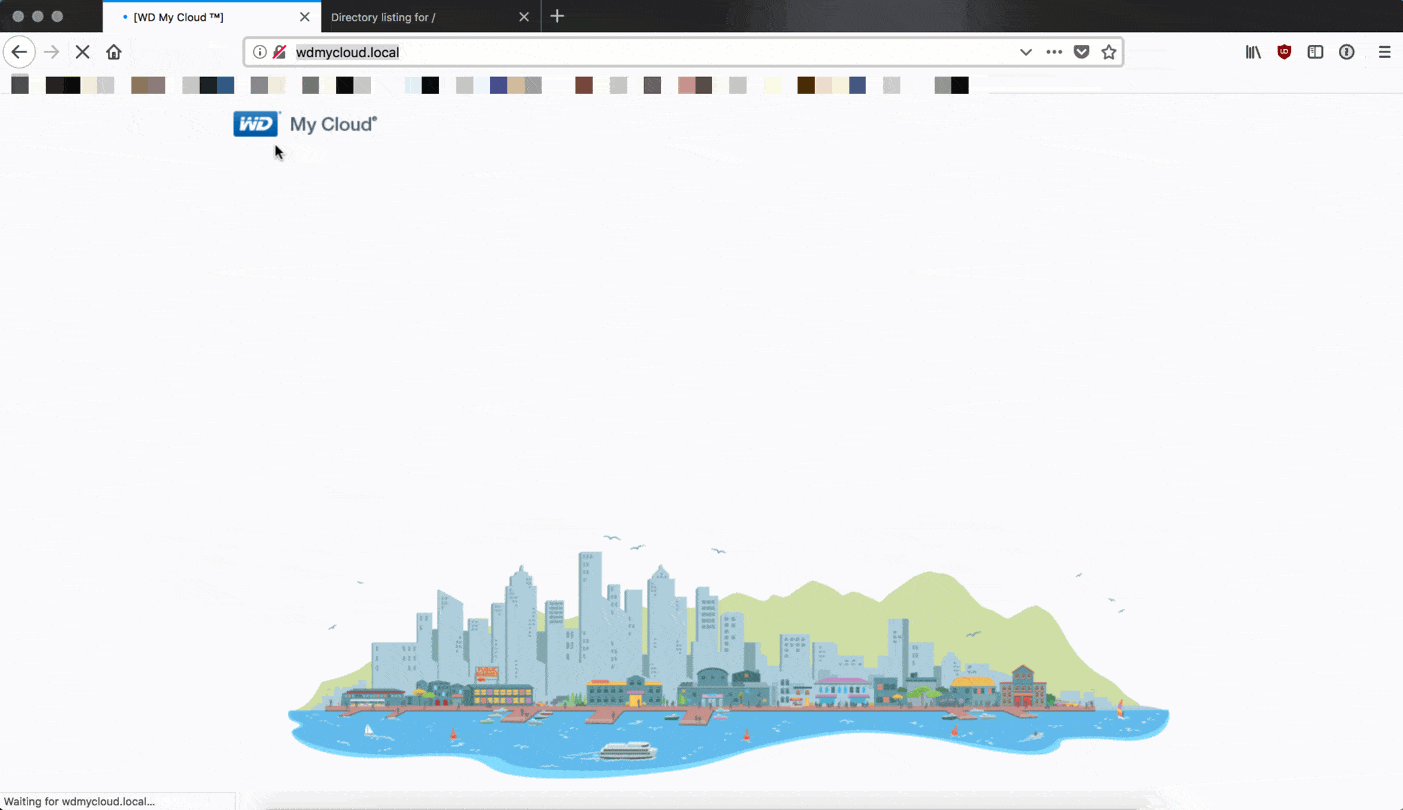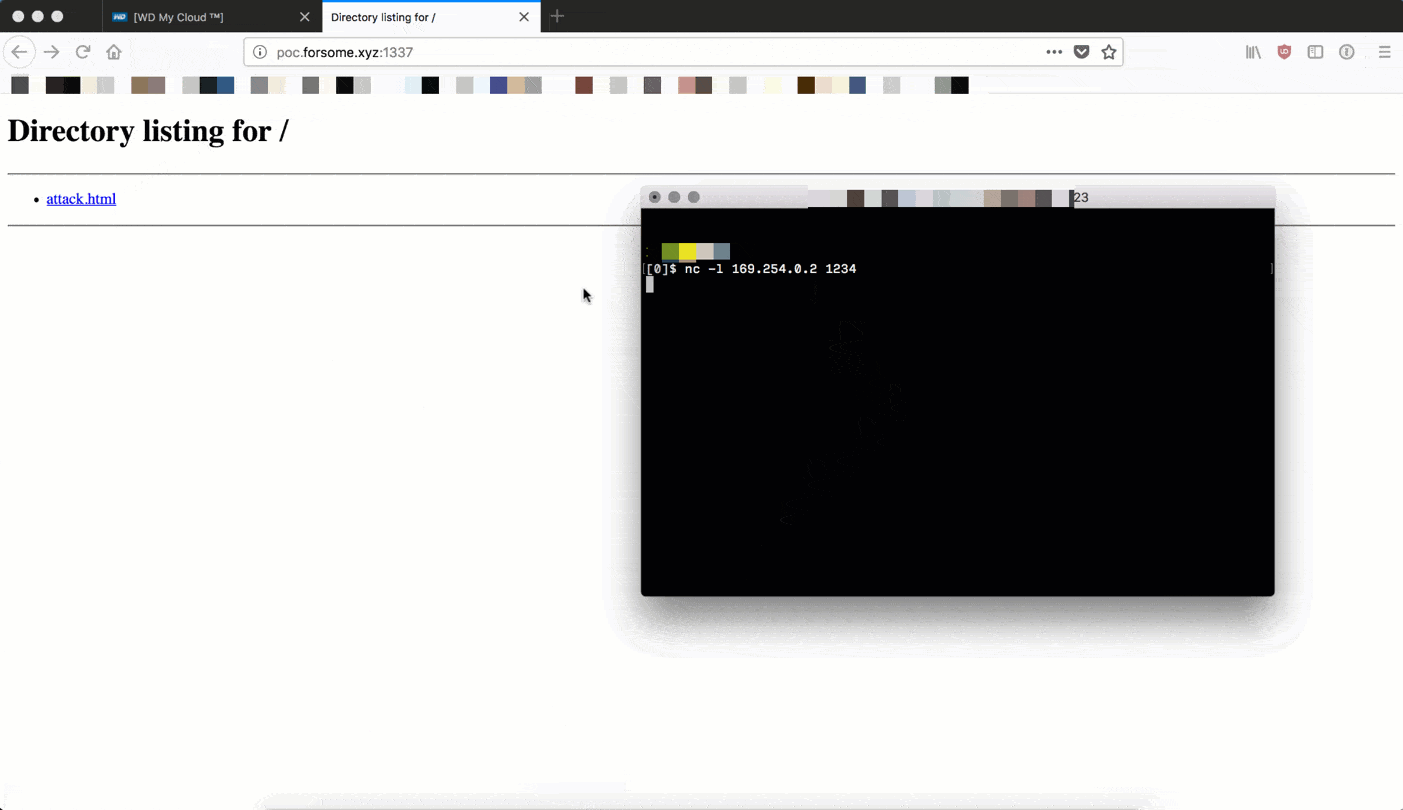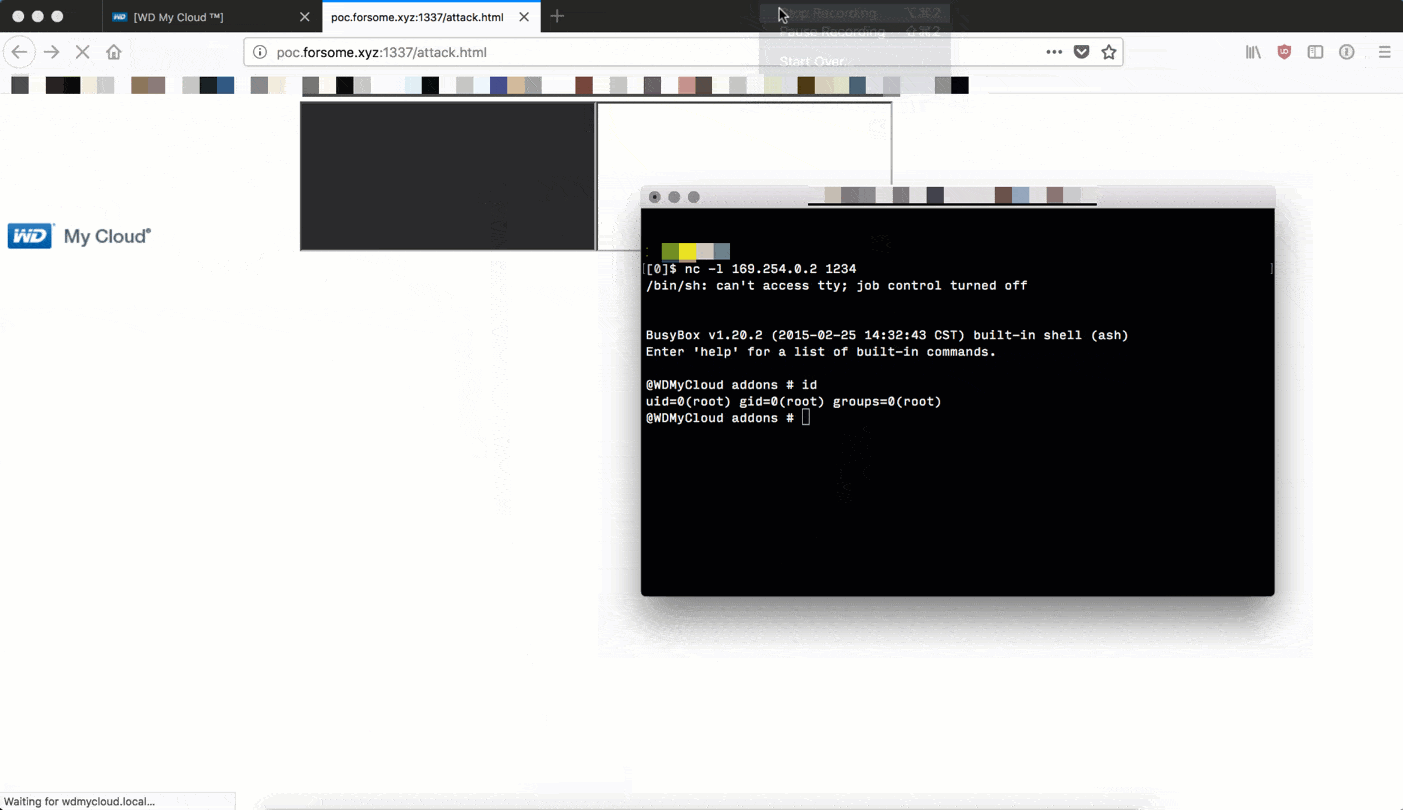
The expert writes that he tested the bug on the Western Digital My Cloud (model WDBCTL0020HWT, firmware 2.30.172), but stresses that the vulnerability is not limited to this model, as all My Cloud products actually use the same vulnerable code.
The problem was discovered while reverse engineering the CGI binary files. It allows an attacker to bypass the authentication mechanism and create an administrator session tied to their IP address. The Securify researchers attached to their report a proof-of-concept exploit that is only a few lines long. It is also noted that the same vulnerability was discovered by the experts at Exploitee.rs, who also published their exploit for free access.
However, the main problem lies not in the vulnerability itself, but in the fact that researchers reported a bug to Western Digital representatives in April 2017, but received no response from the company.
For the time being, there is still no patch for CVE-2018-17153, although after the issues were made public in the media, Western Digital representatives assured that they were already working on a fix and would release a patch within the coming weeks.
Update:
WD developers have released a patch for a dangerous issue.
[“”Hi, just a heads up, the recently reported vulnerability in the My Cloud firmware has been addressed with a user-installable hotfix found here: https://t.co/uplC38HOdt This will be included in an over-the-air update as part of the normal upgrade schedule for these product””]
— Western Digital (@westerndigital) September 21, 2018


