The staff of St. Francis Xavier University in Canada discovered a massive attack on their institution’s network. The attack targeted a hidden cache of cryptocurrency, which is to say it was linked to what is known as cryptojacking.
The unidentified malware that hit the university’s network used the captured computing power to mine bitcoins. As a result, staff were forced to completely “rebuild” the university network to eliminate the infection, following the advice of information security specialists they had consulted.
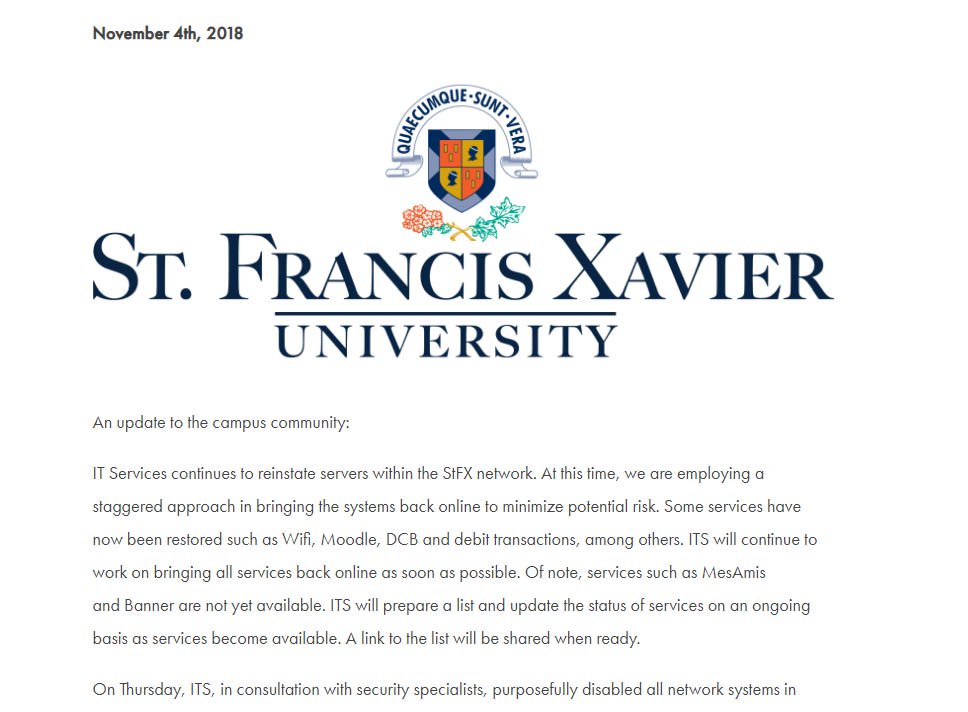
At present, St. Francis Xavier University is recovering from the effects of the attack, but the institution’s network resources have already begun to come back online, including the servers, Wi-Fi and the Moodle educational platform. In addition, the systems that work with students’ payment cards had previously been disabled, and their performance has now been restored.
University representatives stated that they are investigating what happened and that, to date, no evidence has been found of a compromise of the personal data of students or staff.
It should be said that St. Francis Xavier University is not the first victim of malware mining. For example, Imperial College London and even MIT had already been victims of similar attacks, and in both cases, the students themselves tried to use the institution’s facilities to mine cryptocurrency.


