Security and information experts have noticed a new ransomware, Lilocked (aka Lilu), which had already attacked more than 6,000 servers, and it seems the malicious program was designed only for Linux systems.
The first infections were recorded in mid-July 2019; however, it is still unknown exactly how Lilocked gets into its victims’ servers. When the well-known information security specialist Michael Gillespie posted about the ransomware on Twitter, users began reporting that they had been attacked, for example through vulnerabilities in Exim, or damaged by using outdated versions of WordPress.
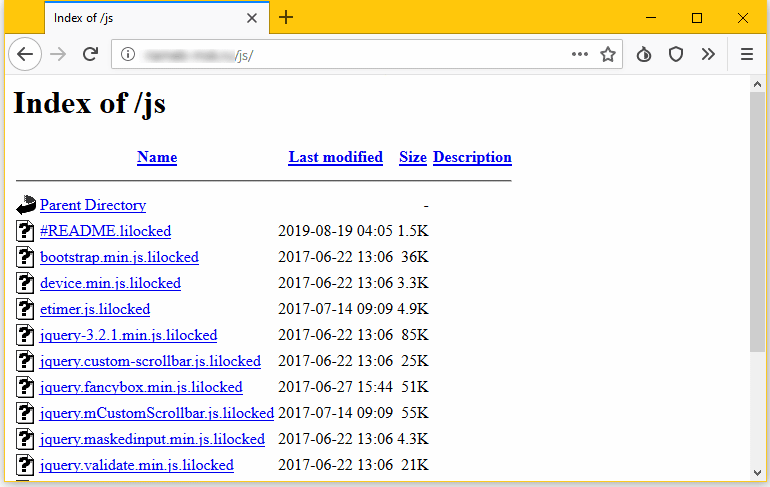
Servers affected by this ransomware are easy to spot, because most of the files they contain are encrypted and carry the .lilocked extension. Researchers note that Lilocked does not encrypt system files so that the server can keep running, but “spoils” HTML, SHTML, JS, CSS, PHP, INI and various image files.
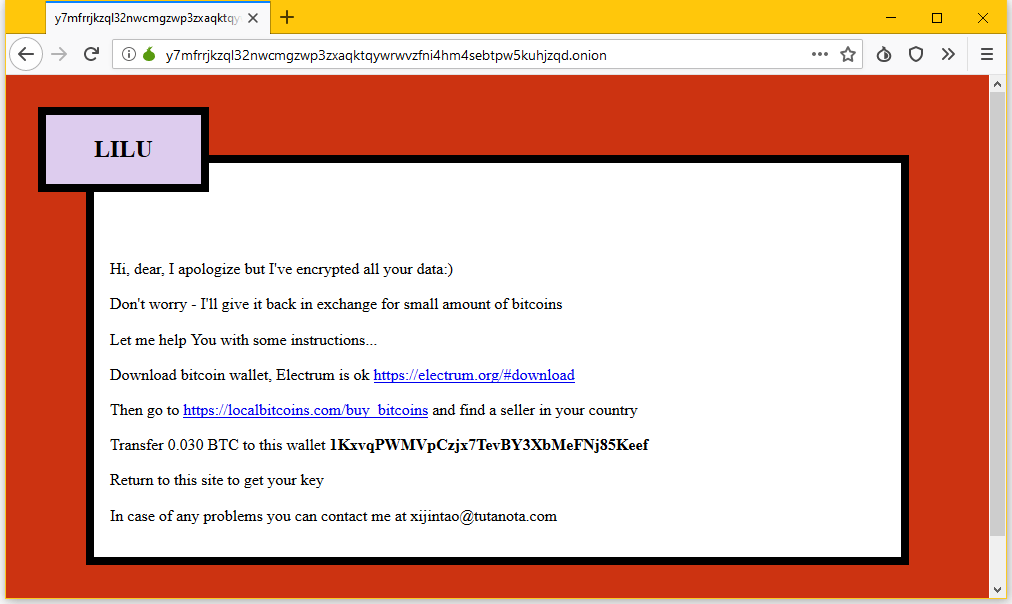
A copy of the ransom demand message (named # README.lilocked) is available in every folder where the ransomware encrypts files. Victims are asked to visit a site on the darknet, where they must enter the note’s key along with the ransom demand. Already here, victims are asked for 0.03 bitcoin (about 325 US dollars at the current rate).
According to the French information security specialist known by the pseudonym Benkow , the ransomware has already hit more than 6,700 servers, many of which are indexed by search engines, making them easy to find via Google.

Unfortunately, the real number of Lilocked victims is likely much higher, since there are very few web servers and many infected systems do not appear in Google search results. It is still unknown how Lilocked works and whether it is possible to recover the affected information without paying a ransom to the attackers, since experts have not yet been able to detect and analyze a sample of the malware.



pas crypter, chiffrer !